Security built into every layer
From the network edge to every staff sign-in, RedCherry protects your brokerage, your team and your clients' data.
How RedCherry protects your brokerage
Protection starts before a request reaches the CRM and continues through every sign-in, permission and change your team makes.
Talk to our team CloudflareCloudflare sits in front of every portal, with DDoS protection on its global network.
- End-to-end encryptionTraffic is encrypted in transit, and sensitive data is stored with AES-256 encryption.
- Two-factor sign-inSign-ins are confirmed with a 6-digit code from an authenticator app.
- IP whitelistingEach staff member can reach the back office only from the IP addresses you approve.
- Roles & permissionsEvery team member gets exactly the access their role needs, and nothing more.
- Audit logsStaff and client activity is logged, so you can see who changed what, and when.
- reCAPTCHABot protection on sign-in and registration.
- Session expiryIdle sessions end on their own, so an unattended screen doesn't stay signed in.
Security for a regulated business
A brokerage's CRM holds identity documents, bank details and trading history, so the controls around it have to satisfy a regulator as well as a security team. RedCherry layers them: Cloudflare in front of every portal with DDoS protection, traffic encrypted in transit and sensitive data stored with AES-256 encryption, and reCAPTCHA on sign-up and sign-in to stop bots.
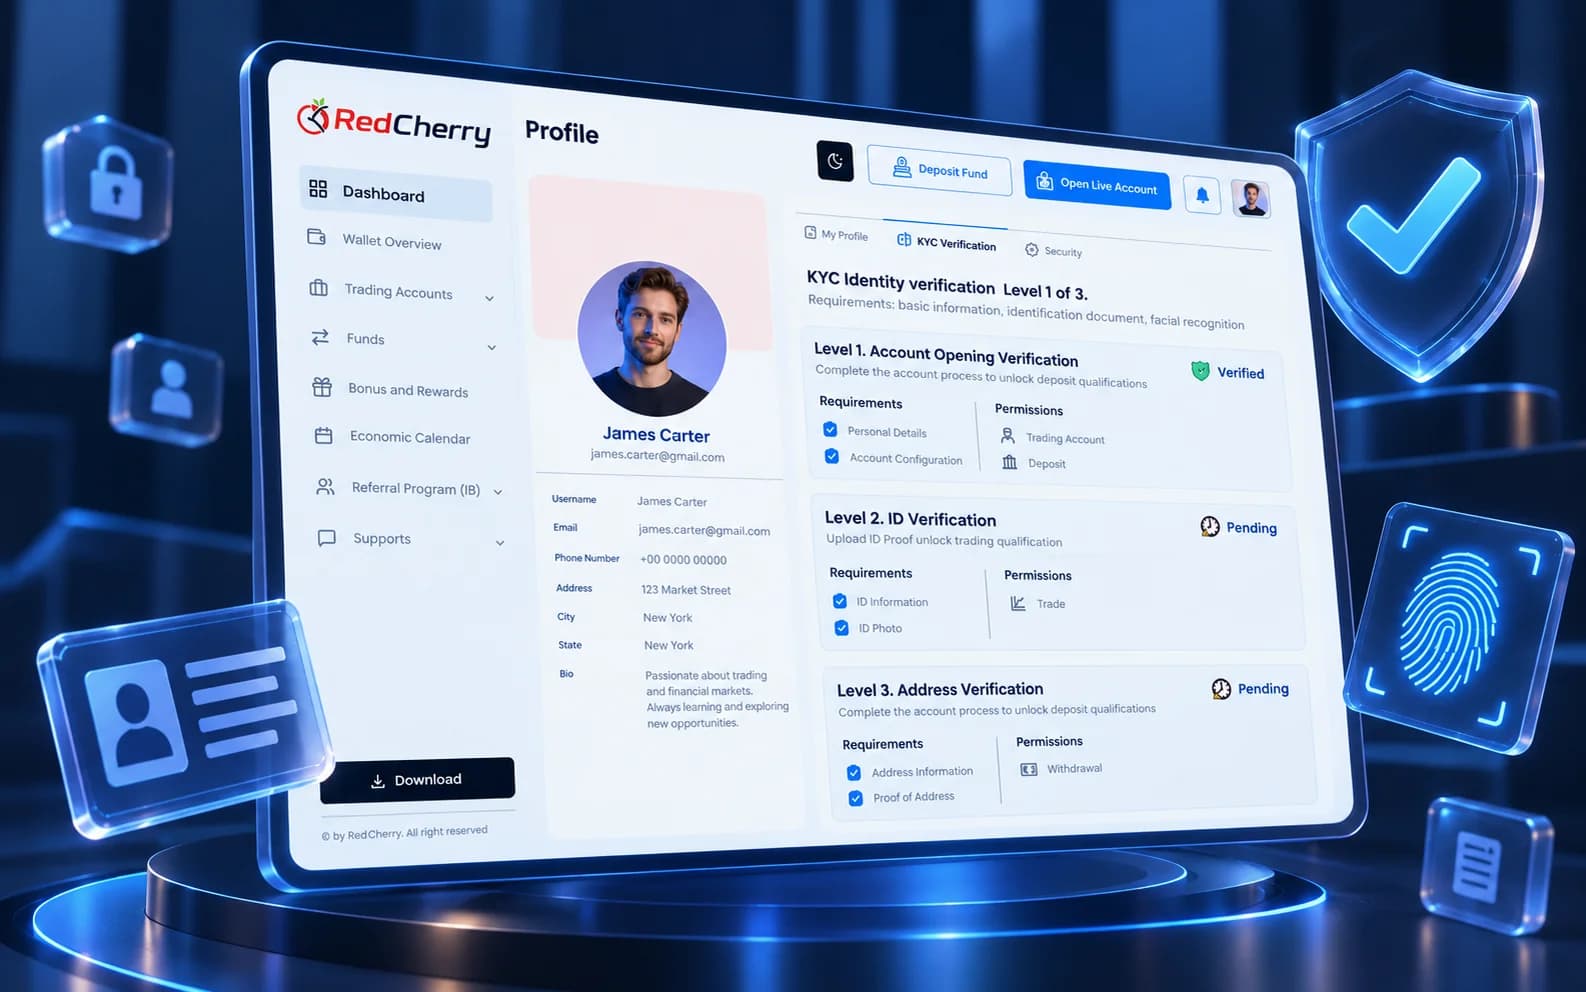
Inside the back office, every staff member signs in with a 6-digit code from an authenticator app, from the IP addresses you approve, with a role that grants exactly the pages and actions their job needs. Idle sessions end on their own, and every staff and client action is written to an audit log, so a compliance review can show who changed what and when. Client-side, verification levels decide what a client can do before and after KYC.
Security questions
Is client data encrypted?
Yes. Traffic between the browser and RedCherry is encrypted in transit, and sensitive data is stored with AES-256 encryption.
Can we limit who reaches the back office?
Yes. Each staff member can be limited to the IP addresses you approve, and sign-ins are confirmed with a code from an authenticator app.
Can we control what each team member can do?
Roles and permissions decide which pages and actions every staff member can use, so each person sees only what their job needs.
Do you keep a record of changes?
Staff and client activity is logged, so you can review who changed what, and when.
How is the platform protected from attacks?
Cloudflare sits in front of every portal with DDoS protection on its global network, and reCAPTCHA protects sign-up and sign-in from bots.
Can you complete our security questionnaire?
Yes. Send it to our team and we will walk your compliance team through how RedCherry is secured.
Running a security review?
Send us your questionnaire and our team will walk your compliance team through how RedCherry is secured.
Talk to our team